Why This Matters
Initia’s decision to halt both its layer-1 chain and every rollup built on it is the real story here, not just the dollar figure. A flaw in how the Initia MoveVM caches scripts let an attacker forge valid-looking contract state, credit themselves with balances the network never actually backed, and move those balances across bridges before anyone could stop them. That a single scripting bug could force a full network stop, across the main chain and its connected rollups, says something about how centralized the failure surface still is in MoveVM-based Layer 1s built for modular rollup ecosystems.
Key Takeaways
- Initia halted its L1 and rollups at 15:41:30 UTC on Oct. 23 after an attacker exploited a MoveVM script-caching flaw, according to Initia via TokenPost.
- The bug let the attacker bypass security checks and forge MoveVM state, crediting themselves with unbacked WETH, iUSD and USDC without changing those tokens’ actual total supply; INIT’s supply was unaffected.
- About $2.7 million left the network before the pause: roughly 105 WETH and 1.4 million AUSD0 via LayerZero, and about 1.08 million USDC via Noble and CCTP, later swapped into 1,135.52 ETH held at a single Ethereum address, per Initia and D2 Finance via Cointelegraph.
- Agora, which issues AUSD, said its contract isn’t deployed on Initia and that a separate third-party adapter using AUSD on Ethereum was the one affected, per cryptowatchdesk.com.
- INIT fell briefly to around $0.115 before rebounding above $0.15 on Friday, trading near $0.1496, according to Cointelegraph.
How the Exploit Worked
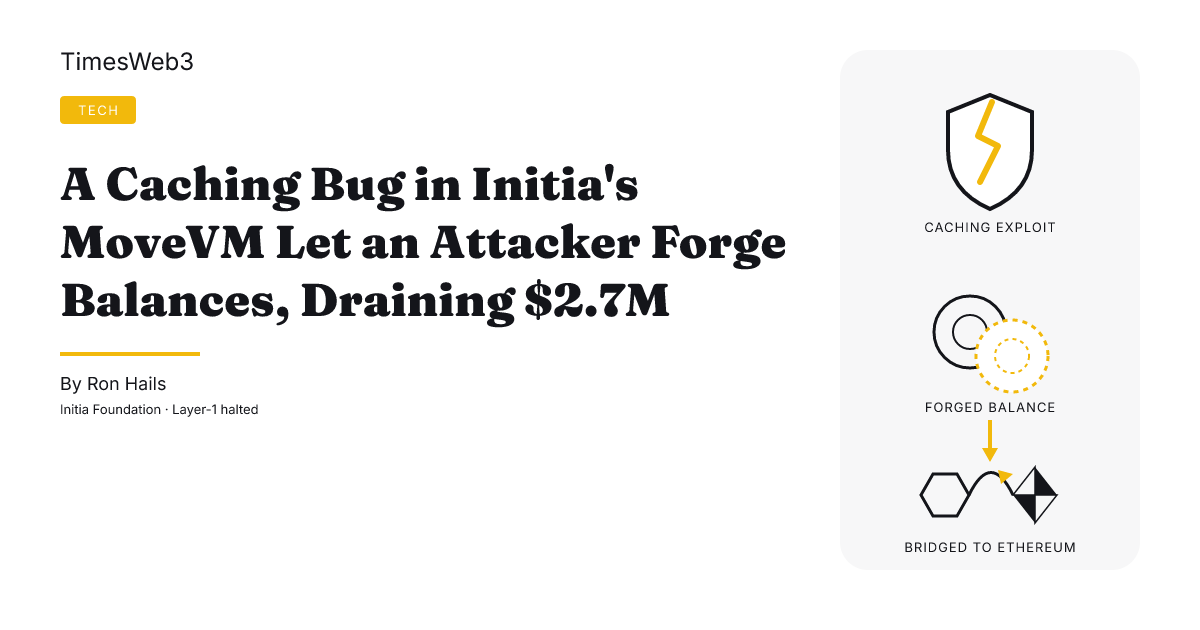
The root cause, as Initia described it, sits in script caching inside its MoveVM, the Move-based execution engine the chain runs on top of the Cosmos SDK. Script caching is meant to speed up repeated contract calls by storing validated execution paths rather than re-checking them every time. Initia said the attacker found a way to exploit that caching layer to bypass the checks that would normally stop someone from crediting themselves with tokens they never deposited, effectively forging MoveVM state, per Initia’s disclosure reported by TokenPost and chaincatcher.com.
Critically, Initia said the forged balances in WETH, iUSD and USDC did not change those tokens’ real total supply on their native chains, and no INIT was minted at all. That distinction matters for scope: this wasn’t a mint-at-the-source attack on INIT’s monetary base. It was a local accounting forgery on Initia that only became real money once the attacker pushed the forged balances through bridges to Ethereum.
Engineer Zon, whose analysis Initia reposted, described it as a “Day 0 bug” specific to Initia’s MoveVM implementation that let the attacker mint extra tokens on the main chain without touching native INIT, according to cryptowatchdesk.com.
The Timeline From Mint to Pause
On-chain analysis from D2 Finance, cited by cryptowatchdesk.com and Cointelegraph, lays out how fast the forged balances turned into real assets. At 14:59:26 UTC on Oct. 23, one transaction on Initia minted 2,000,000 tokens of a bridged AUSD representation. By 15:01:59, the corresponding LayerZero bridge contract on Ethereum released 1.4 million real AUSD. At 15:06:47, 105 ETH left the same way. Security researcher Spreek publicly flagged the outflow at 15:27, putting the loss at roughly $2.6 million at that point. Initia halted the chain at 15:41:30 and posted the halt notice around 16:00.
D2 Finance said it traced about $2.65 million back onto Ethereum within roughly seven minutes of the initial mint. Separately, about 1.08 million USDC moved out through Noble and CCTP. Initia said all of the proceeds were ultimately exchanged for 1,135.52 ETH, now sitting in a single Ethereum wallet, a figure both Initia and chaincatcher.com put at the address 0x358ef0130f7a5aa516dcd81bdc80b18cde41cac8.
Who Actually Bears the Loss
Outlets diverge on where the financial damage lands, and that gap got corrected in real time. D2 Finance’s initial read implied AUSD itself had been minted without backing. Agora, the issuer of AUSD, pushed back directly, telling cryptowatchdesk.com that its contract “is not deployed on Initia” and that “a separate, third-party product not operated by Agora that uses AUSD on Ethereum was impacted.” Agora added that AUSD “is fully backed.” D2 revised its own post to match, stating the loss “sits with the adapter’s depositors,” meaning people who had locked real AUSD into that third-party bridge contract on Ethereum rather than AUSD holders broadly.
Initia itself has stayed narrower in what it will confirm. It has verified the halt, the Oct. 23 timing, the script-caching root cause, and the roughly $2.7 million transferred out. It has not yet said who ultimately absorbs that loss.
What to Watch
Initia said a security fix should be completed and audited “within days,” but it has not given a restart date for its L1 or its rollups, which remain paused as of this reporting. The company also committed to publishing a full postmortem once recovery work with its security partners concludes. Separately, INIT’s price swung from roughly $0.115 to above $0.15 on Friday and was trading near $0.1496 at last check, a reminder that the token market has already started pricing in how the incident gets resolved even before Initia’s own investigation is finished, according to Cointelegraph.
Sources
- TokenPost: Initia Says MoveVM Flaw Enabled About $2.7M in Transfers
- cryptowatchdesk.com: Security Alert: Initia halts its chain after a minting bug lets $2.7 million out
- Cointelegraph: Initia halts blockchain after exploit reportedly drains over $2.6M
- chaincatcher.com: Initia disclosed attack details: MoveVM cache vulnerability caused approximately 2.7 million USD to be transferred out